
Operating System
Data breaches cost businesses billions annually—but most threats originate internally. These 10 proven internal safeguards help cybersecurity experts lock down company data before vulnerabilities escalate into catastrophic leaks.
Zero Trust Network Access Implementation
Forget relying on outdated perimeter defenses—Zero Trust Network Access (ZTNA) flips the script by assuming every user and device is a potential threat, no matter where they’re logging in from. This model replaces the old "trust but verify" approach with continuous verification, ensuring only authenticated and authorized entities access your network resources.
With ZTNA, you enforce least-privilege access by default, using multi-factor authentication (MFA) and device posture checks before granting entry. Solutions like Cloudflare Access or Zscaler Private Access integrate seamlessly with existing identity providers (IdP) such as Okta or Azure AD, while micro-segmentation isolates critical assets. The result? Reduced attack surfaces and real-time threat detection, even for remote teams.
Perfect for companies with hybrid or fully remote workforces, ZTNA adapts to modern threats—like credential stuffing or insider risks—without sacrificing usability. ⚡
Automated Data Loss Prevention Systems
Forget relying on employee vigilance alone—automated Data Loss Prevention (DLP) systems act as an invisible bouncer, stopping sensitive files from slipping out via email, cloud uploads, or USB drives. Unlike Zero Trust (which focuses on access control), DLP specializes in real-time content inspection, scanning for credit card numbers, Social Security digits, or proprietary documents before they leave your network.
Top solutions like Symantec DLP or Forcepoint integrate with Microsoft 365 and SharePoint to flag violations instantly, with customizable policies for industries like healthcare (HIPAA) or finance (PCI DSS). The best systems even block encrypted traffic when anomalies are detected, ensuring compliance without sacrificing productivity. Deployment typically takes under 30 days for mid-sized businesses.
This is non-negotiable for legal firms, R&D labs, or any team handling trade secrets or client PII. The peace of mind alone makes it worth the investment. ✨
Role-Based Access Control (RBAC) Policies
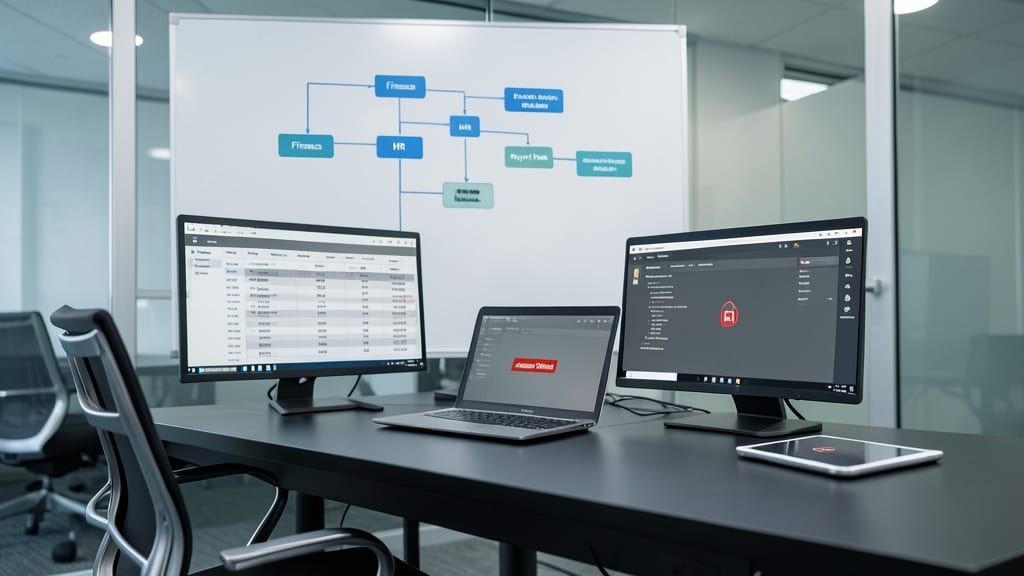
What if your finance team could only access payroll data, while HR never sees customer records? That’s the power of Role-Based Access Control (RBAC), where permissions align exactly with job functions—no extra, no less.
RBAC frameworks like Microsoft Active Directory or Okta assign granular permissions (e.g., read-only vs. edit access) based on roles like "Manager," "Developer," or "Intern." This isn’t just about locking doors—it’s about audit trails that track who accessed what, when, and why. Studies show 68% of breaches involve internal actors, but RBAC cuts that risk by ensuring employees only see what they need to do their jobs.
Perfect for mid-sized businesses or departments handling sensitive data—like legal or R&D—where accidental leaks or malicious intent could derail operations. Implementing RBAC starts with mapping roles to data needs, then enforcing those rules consistently. 💻
Endpoint Detection and Response (EDR) Tools
While RBAC and DLP focus on permissions and data leaks, Endpoint Detection and Response (EDR) acts like a cybersecurity guard dog—patrolling every device in your network 24/7. Unlike traditional antivirus, EDR doesn’t just scan for known malware; it uses AI-driven behavioral analysis to detect anomalies like unauthorized data transfers, lateral movement by attackers, or even zero-day exploits attempting to execute.
Top solutions like CrowdStrike Falcon or Microsoft Defender for Endpoint provide real-time threat hunting, automated containment (quarantining infected machines instantly), and detailed forensic reports to trace attack origins. They integrate with SIEM tools for centralized monitoring, making it easier to correlate endpoint alerts with broader network threats. For environments with mixed Windows/Linux endpoints, EDR ensures no device flies under the radar.
This is your first line of defense against supply-chain attacks or insider threats—ideal for finance, healthcare, or any industry where a single compromised device could trigger a full-scale breach. 💪
Multi-Factor Authentication for All Systems
Credential stuffing attacks are on the rise, with hackers using stolen passwords to breach accounts in seconds—but multi-factor authentication (MFA) adds a second (or third) layer of defense that’s nearly impossible to bypass.
Modern MFA solutions like Duo Security, Microsoft Authenticator, or YubiKey integrate seamlessly with Active Directory, Azure AD, and cloud apps, requiring users to verify identity via push notifications, biometrics, or hardware tokens after entering a password. This stops automated attacks cold, even if passwords are compromised. For legacy systems lacking native MFA, third-party adapters bridge the gap without forcing a full platform overhaul.
Teams handling sensitive data—think finance, healthcare, or legal—should prioritize FIDO2-compliant MFA for its phishing-resistant design. Even small businesses benefit from zero-configuration setups like Google’s Titan Security Key, which plugs into any USB port. 🔧
Regular Security Awareness Training Programs
Did you know 95% of cybersecurity breaches start with human error? Security awareness training closes that gap by turning employees into your first line of defense against phishing, social engineering, and credential theft.
Modern programs go beyond generic slideshows, using simulated phishing attacks to test real-world reactions and interactive modules that adapt to individual skill levels. Platforms like KnowBe4 or Security Awareness Training Company offer gamified learning with leaderboards, quizzes, and role-specific scenarios—making retention rates soar. The best programs also include quarterly refreshers and incident-specific follow-ups to keep defenses sharp.
This isn’t just for IT teams—every department benefits. Finance staff learn to spot CEO fraud schemes, HR teams recognize resume scams, and executives avoid tailored spear-phishing. Start with a baseline assessment to identify weak spots, then roll out training in bite-sized sessions. 💡
Encrypted Database and File Storage
When a stolen laptop or compromised server becomes the weak link in your security chain, encrypted database and file storage acts as your last line of defense. Unlike perimeter defenses or user training, this safeguard ensures your data remains unreadable even if attackers bypass every other layer.
Solutions like AWS KMS, Microsoft Azure Key Vault, or VeraCrypt provide AES-256 encryption—the gold standard for securing databases and files at rest. For transit, TLS 1.3 ensures data stays encrypted while moving between servers, endpoints, or cloud services. The best systems also support key rotation, so compromised keys can’t be reused indefinitely.
This is non-negotiable for healthcare providers handling PHI, financial institutions managing PII, or any business storing sensitive intellectual property. Even if a breach occurs, encrypted storage ensures attackers walk away with nothing but gibberish. ✨
Privileged Access Management (PAM) Solutions
Cybercriminals don’t just target random employees—they go after administrator accounts with broad access. Privileged Access Management (PAM) solutions like CyberArk or Thycotic lock down these high-risk accounts by granting access only when needed (just-in-time), then revoking it immediately after.
These tools provide session monitoring, multi-factor authentication for admins, and detailed audit logs to track every privileged action. For example, BeyondTrust offers automated password rotation and privileged session isolation, ensuring even if credentials are compromised, attackers can’t escalate their access undetected. The best PAM systems integrate with SIEM tools for real-time threat detection.
Ideal for IT admins, DevOps teams, and compliance officers, PAM is non-negotiable for industries like finance or healthcare where HIPAA/GDPR compliance demands strict access controls. ⚡
Automated Patch Management Systems
Forget waiting for security alerts—automated patch management systems proactively close vulnerabilities before attackers even find them. These tools scan your entire environment, prioritize critical updates, and deploy patches across servers, endpoints, and IoT devices with minimal manual intervention.
Solutions like SolarWinds Patch Manager or ManageEngine Patch Manager Plus integrate with vulnerability databases to identify zero-day risks, schedule updates during off-hours, and generate compliance reports for audits. The best systems even test patches in sandbox environments first to avoid compatibility issues. With 90% of breaches linked to unpatched software, automation isn’t just efficient—it’s a survival tactic. 💪
Incident Response and Recovery Plans
When a breach happens, every minute counts—yet many companies scramble without a predefined incident response plan. A well-documented Incident Response and Recovery Plan (IRRP) turns chaos into structured action, ensuring you contain threats within hours, not days. Tools like Splunk Enterprise Security or IBM QRadar integrate with SIEM systems to automate threat detection and trigger predefined playbooks, reducing manual response time by up to 70%.
These plans include step-by-step containment protocols, forensic investigation checklists, and escalation paths for legal/compliance teams. For example, NIST’s SP 800-61 framework provides a battle-tested template covering detection, analysis, containment, eradication, and recovery phases. Automated recovery workflows—like AWS Backup or Veeam—ensure critical systems restore from air-gapped backups in minutes, not hours.
Best for regulated industries (healthcare, finance) or businesses handling sensitive data, an IRRP isn’t just a compliance checkbox—it’s your financial lifeline. Without it, the average breach costs $4.45 million; with one, you slash that by cutting downtime in half. 💪